

Verified NSE7_SDW-6.4 Exam Dumps Q&As - Provide NSE7_SDW-6.4 with Correct Answers
Pass Your NSE7_SDW-6.4 Dumps Free Latest Fortinet Practice Tests
Fortinet NSE7_SDW-6.4 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
NEW QUESTION 16
Which statement defines how a per-IP traffic shaper of 10 Mbps is applied to the entire network?
- A. Each IP is guaranteed a minimum 10 Mbps of bandwidth
- B. A single user uses the allocated bandwidth divided by total number of users.
- C. The 10 Mbps bandwidth is shared equally among the IP addresses.
- D. FortiGate allocates each IP address a maximum 10 Mbps of bandwidth.
Answer: D
NEW QUESTION 17
Which two statements reflect the benefits of implementing the ADVPN solution to replace conventional VPN topologies? (Choose two )
- A. It ensures that spoke-to-spoke traffic no longer needs to flow through the tunnels through the hub
- B. It provides direct connectivity between all sites by creating on-demand tunnels between spokes.
- C. It creates redundant tunnels between hub-and-spokes, in case failure takes place on the primary links
- D. It dynamically assigns cost and weight between the hub and the spokes, based on the physical distance
Answer: A,C
NEW QUESTION 18
Refer to exhibits.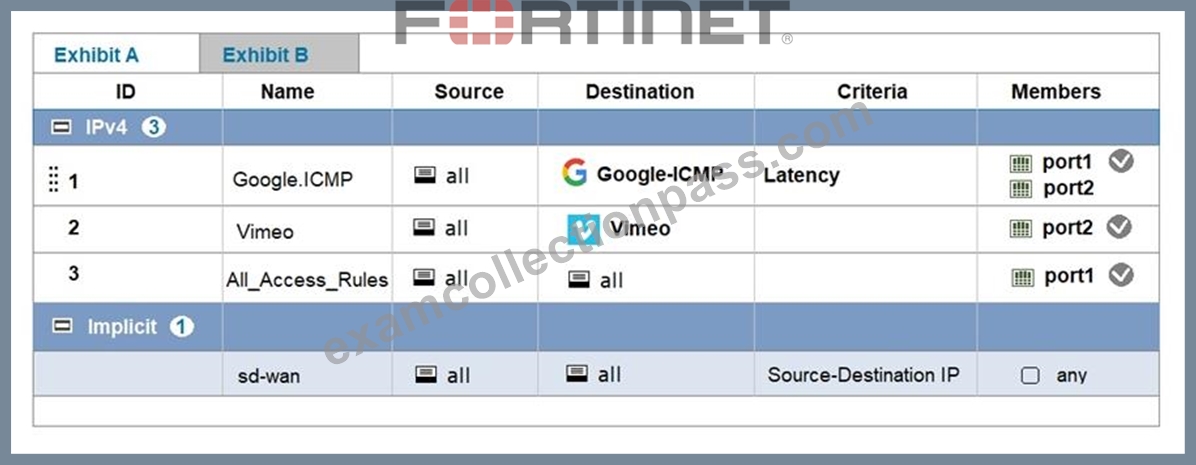
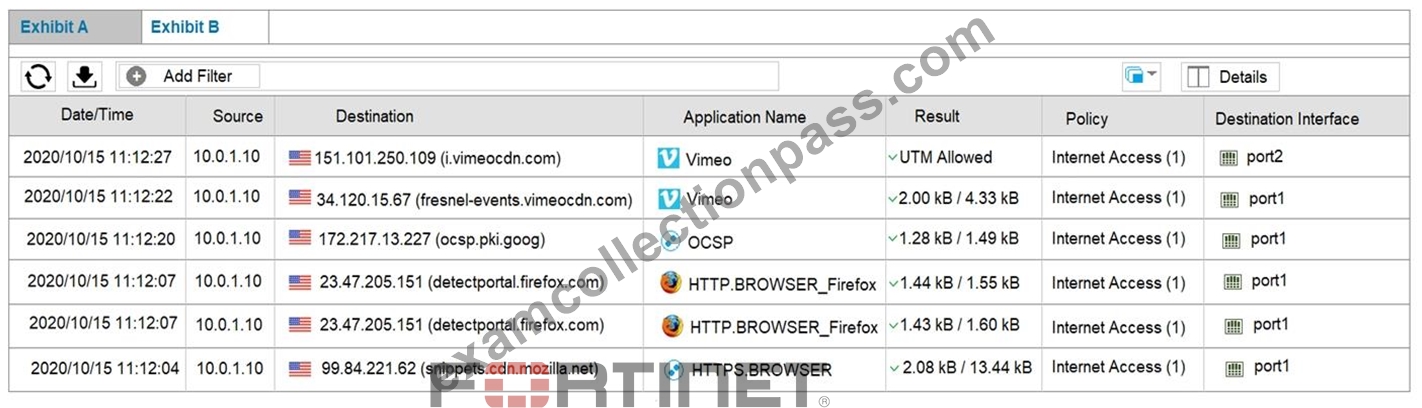
Exhibit A shows the SD-WAN rules and exhibit B shows the traffic logs. The SD-WAN traffic logs reflect how FortiGate processed traffic.
Which two statements about how the configured SD-WAN rules are processing traffic are true? (Choose two.)
- A. The initial session of an application goes through a learning phase in order to apply the correct rule.
- B. The All_Access_Rules rule load balances Vimeo application traffic among SD-WAN member interfaces.
- C. SD-WAN rules are evaluated in the same way as firewall policies: from top to bottom.
- D. The implicit rule overrides all other rules because parameters widely cover sources and destinations.
Answer: C,D
NEW QUESTION 19
Which statement is correct about the SD-WAN and ADVPN?
- A. Spoke support dynamic VPN as a static interface.
- B. Dynamic VPN is not supported as an SD-Wan interface.
- C. Hub FortiGate is limited to use ADVPN as SD-WAN member interface.
- D. ADVPN interface can be a member of SD-WAN interface.
Answer: D
NEW QUESTION 20
Refer to the exhibit.
Multiple IPsec VPNs are formed between two hub-and-spokes groups, and site-to-site between Hub 1 and Hub 2 The administrator configured ADVPN on the dual regions topology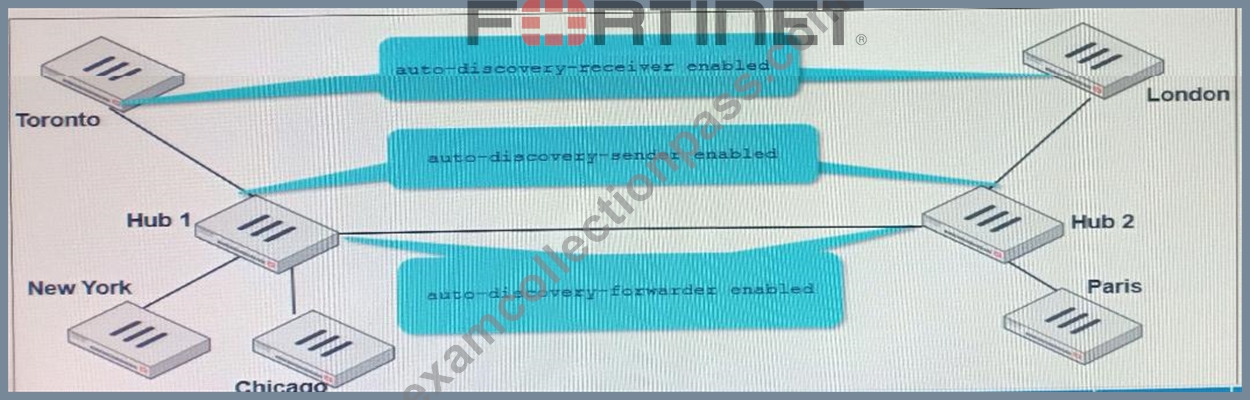
Which two statements are correct if a user in Toronto sends traffic to London? (Choose two )
- A. London generates an IKE information message that contains the Toronto public IP address
- B. Toronto needs to establish a site-to-site tunnel with Hub 2 to bypass Hub 1.
- C. Traffic from Toronto to London triggers the dynamic negotiation of a direct site-to-site VPN
- D. The first packets from Toronto to London are routed through Hub 1 then to Hub 2.
Answer: B,C
NEW QUESTION 21
Refer to the exhibit.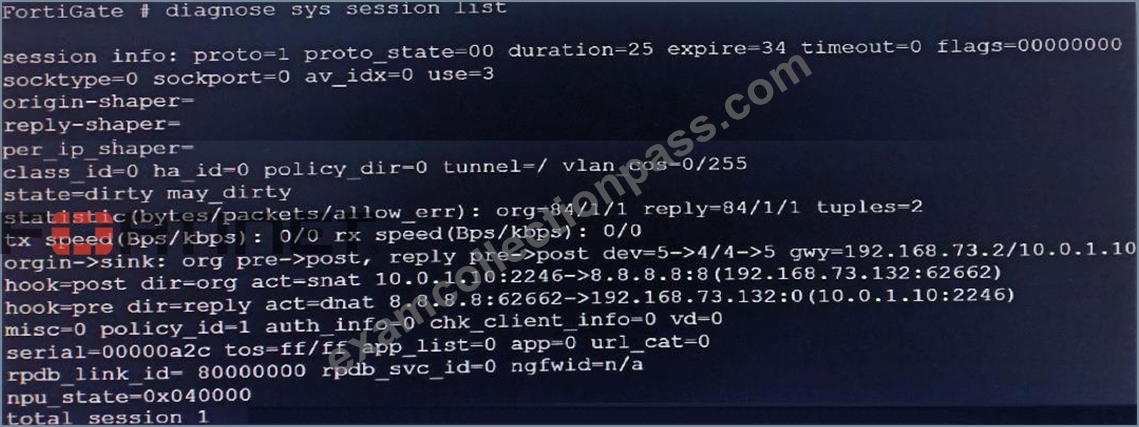
Based on the exhibit, which statement about FortiGate re-evaluating traffic is true?
- A. The type of traffic defined and allowed on firewall policy ID 1 is UDP.
- B. FortiGate has terminated the session after a change on policy ID 1.
- C. Firewall policy ID 1 has source NAT disabled.
- D. Changes have been made on firewall policy ID 1 on FortiGate.
Answer: D
NEW QUESTION 22
Which components make up the secure SD-WAN solution?
- A. FortiGate, FortiManager, FortiAnalyzer, and FortiDeploy
- B. Datacenter, branch offices, and public cloud
- C. Telephone, ISDN, and telecom network.
- D. Application, antivirus, and URL, and SSL inspection
Answer: D
NEW QUESTION 23
Refer to the exhibit.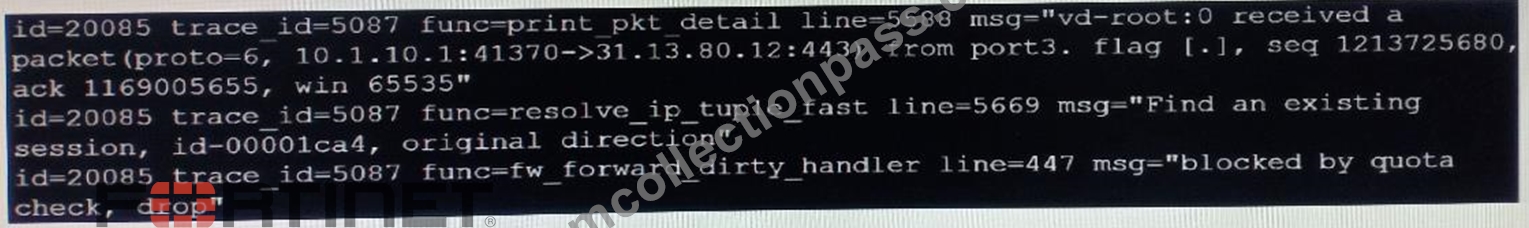
Which statement about the trace evaluation by FomGate is true?
- A. Packets exceeding the configured concurrent connection limit are dropped based on the priority configuration.
- B. The packet exceeded the configured maximum bandwidth and was dropped by the shared shaper.
- C. Packets exceeding the configured maximum concurrent connection limit are denied by the per-IP shaper.
- D. The packet exceeded the configured bandwidth and was dropped based on the priority configuration.
Answer: C
NEW QUESTION 24
What are two roles that SD-WAN orchestrator plays when it works with FortiManager? (Choose two.)
- A. It acts as a hub FortiGate with an SD-WAN interface enabled and managed along with other FortiGate devices by FortiManager.
- B. It configures and monitors SD-WAN networks on FortiGate devices that are managed by FortiManager.
- C. It acts as an application that is released and signed by Fortinet to run as a part of management extensions on FortiManager.
- D. It acts as a standalone device to assist FortiManager to manage SD-WAN interfaces on the managed FortiGate devices.
Answer: C,D
Explanation:
Explanation/Reference:
NEW QUESTION 25
What are two benefits of using FortiManager to organize and manage the network for a group of FortiGate devices? (Choose two )
- A. It improves SD-WAN performance on the managed FortiGate devices.
- B. It reduces WAN usage on FortiGate devices by acting as a local FortiGuard server.
- C. It simplifies the deployment and administration of SD-WAN on managed FortiGate devices.
- D. It sends probe signals as health checks to the beacon servers on behalf of FortiGate.
- E. It acts as a policy compliance entity to review all managed FortiGate devices.
Answer: A,E
NEW QUESTION 26
Refer to exhibits.
Exhibit A.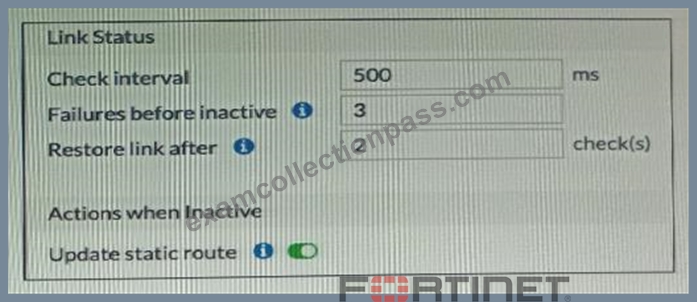
Exhibit B.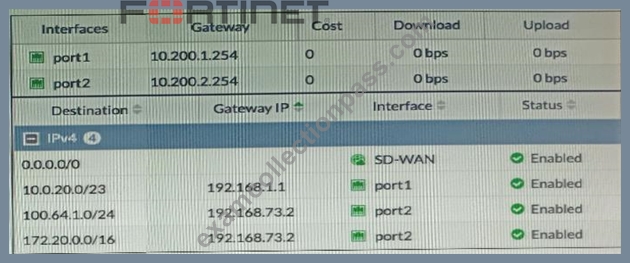
Exhibit A shows the SD-WAN performance SLA and exhibit B shows the SO-WAN interface and the static routes configuration.
Port1 and port2 are member interfaces of the SD-WAN, and port2 becomes a dead member after reaching the failure thresholds Which statement about the dead member is correct?
- A. Dead members require manual administrator access to bring them back alive
- B. Port2 might become alive when a single response is received from an SLA server
- C. Subnets 100 .64.1.0/23 and 172 . 20 . 0. 0/16 are reachable only through port1
- D. SD-WAN interface becomes disabled and port1 becomes the WAN interface
Answer: C
NEW QUESTION 27
Refer to the exhibit.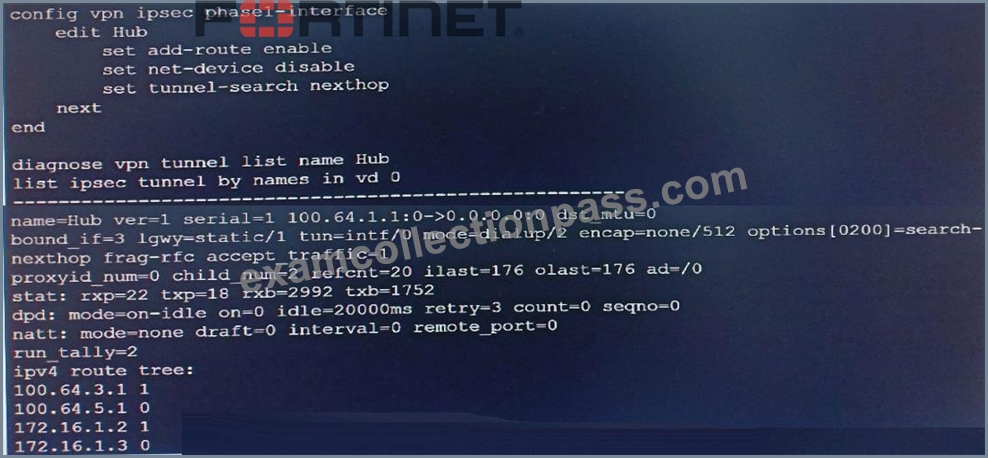
Which two statements about the status of the VPN tunnel are true? <Choose two )
- A. There are separate virtual interfaces for each dial-up client.
- B. FortiGate created a single IPsec virtual interface that is shared by all clients.
- C. VPN static routes are prevented from populating the FortiGate routing table.
- D. 100.64.3.1 is one of the remote IP address that comes through index interface 1.
Answer: B,D
NEW QUESTION 28
Refer to the exhibit.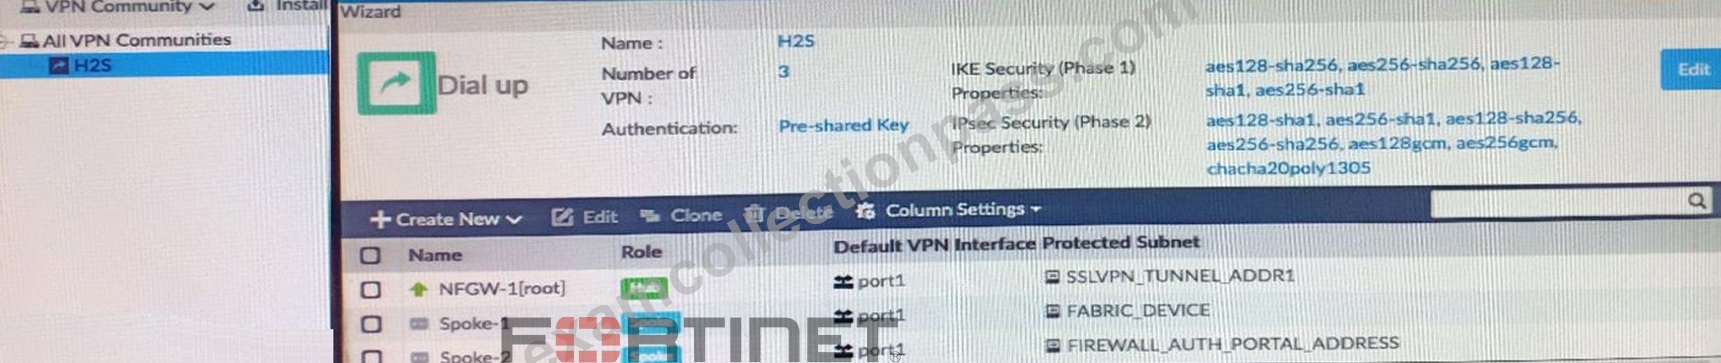
What must you configure to enable ADVPN?
- A. On the hub VPN, only the device needs additional phase one sett
- B. Each VPN device has a unique pre-shared key configured separately on phase one
- C. The protected subnets should be set to address object to all (0.0 .0. o/o).
- D. ADVPN should only be enabled on unmanaged FortiGate devices.
Answer: B
NEW QUESTION 29
What are two roles that SD-WAN orchestrator plays when it works with FortiManager? (Choose two )
- A. It acts as a hub FortiGate with an SD-WAN interface enabled and managed along with other FortiGate devices by FortiManager.
- B. It configures and monitors SD-WAN networks on FortiGate devices that are managed by FortiManager.
- C. It acts as an application that is released and signed by Fortinet to run as a part of management extensions on FortiManager.
- D. It acts as a standalone device to assist FortiManager to manage SD-WAN interfaces on the managed FortiGate devices.
Answer: C,D
NEW QUESTION 30
Refer to exhibits.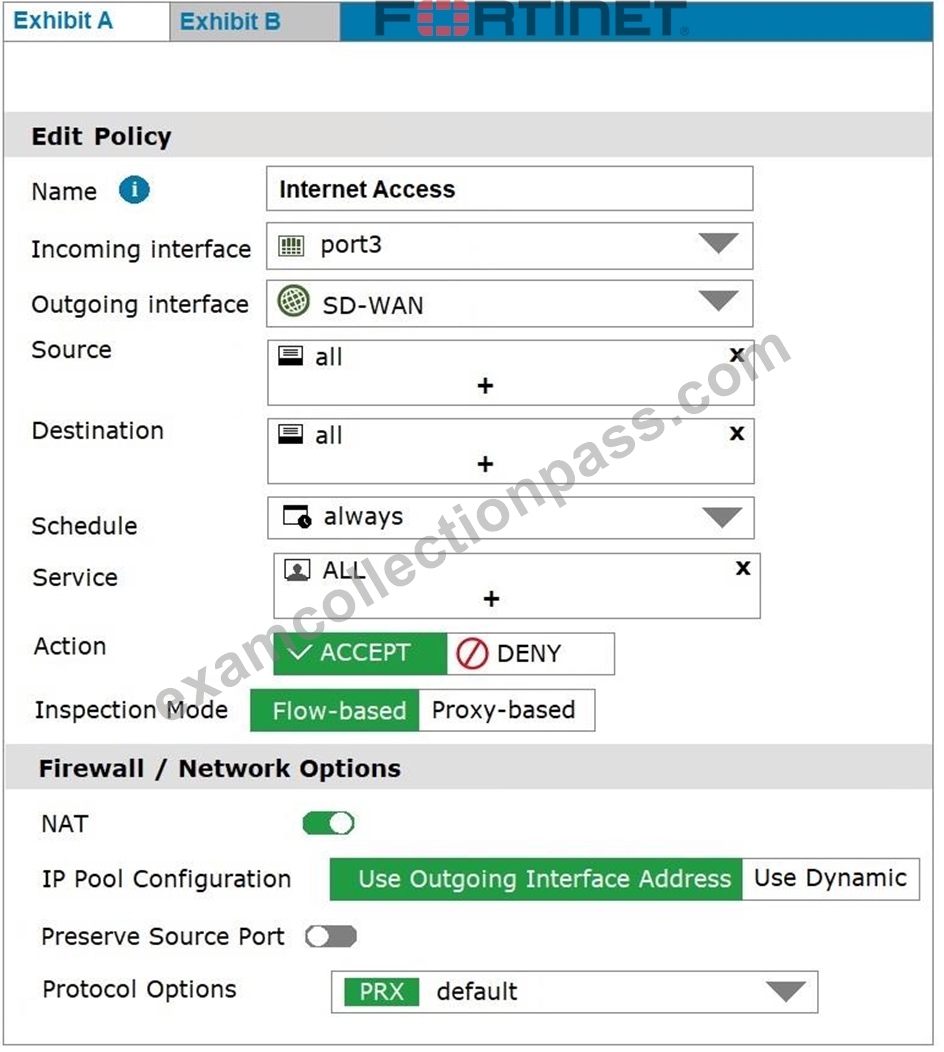
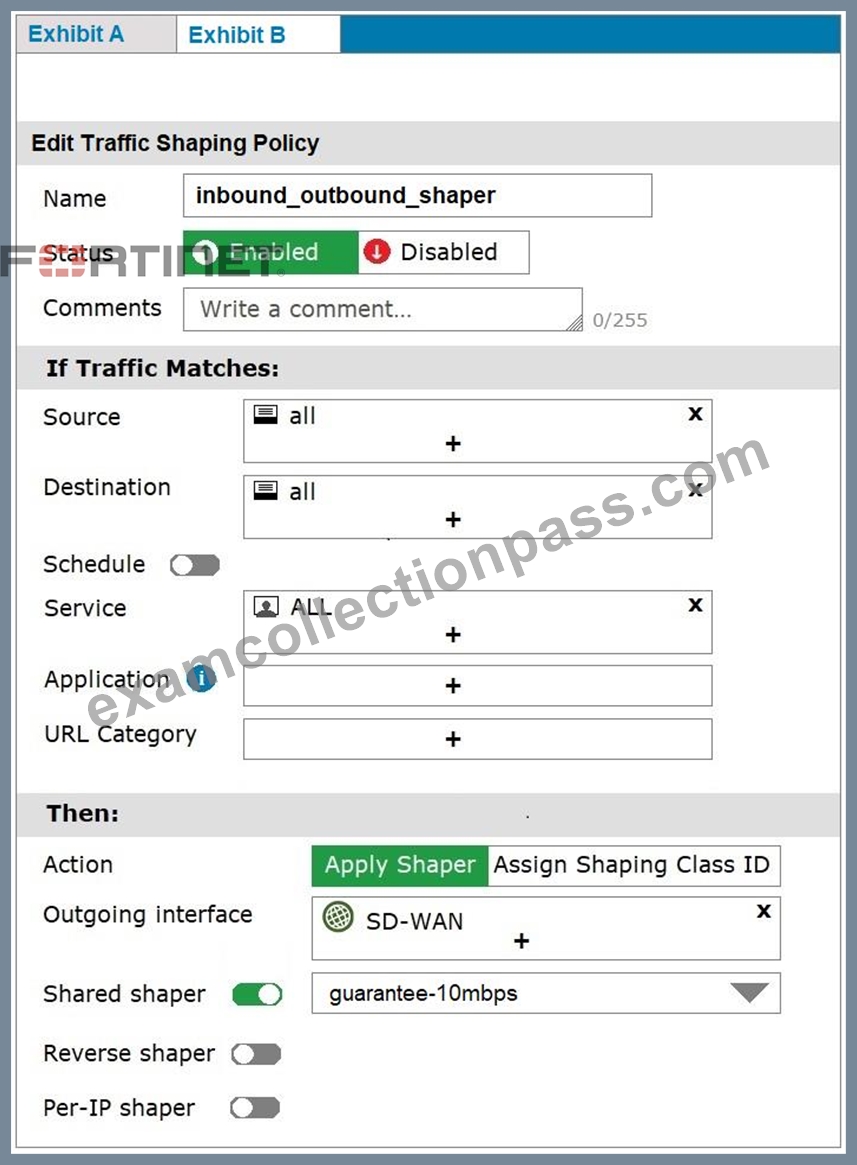
Exhibit A shows the firewall policy and exhibit B shows the traffic shaping policy.
The traffic shaping policy is being applied to all outbound traffic; however, inbound traffic is not being evaluated by the shaping policy.
Based on the exhibits, what configuration change must be made in which policy so that traffic shaping can be applied to inbound traffic?
- A. The reverse shaper option must be enabled and a traffic shaper must be selected
- B. The guaranteed-10mbps option must be selected as the reverse shaper option.
- C. The guaranteed-10mbps option must be selected as the per-IP shaper option
- D. A new firewall policy must be created and SD-WAN must be selected as the incoming interface.
Answer: B
NEW QUESTION 31
Refer to exhibits.
Exhibit A.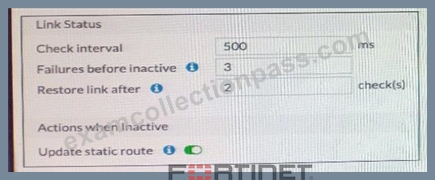
Exhibit B.
Exhibit A, which shows the SD-WAN performance SLA and exhibit B shows the health of the participating SD-WAN members.
Based on the exhibits, which statement is correct?
- A. The dead member interface stays unavailable until an administrator manually brings the interface back.
- B. Check interval is the time to wait before a packet sent by a member interface considered as lost.
- C. The SLA state of port2 has exceeded three consecutive unanswered requests from the SLA server.
- D. Port2 needs to wait 500 milliseconds to change the status from alive to dead.
Answer: C
NEW QUESTION 32
Refer to exhibits.
Exhibit A.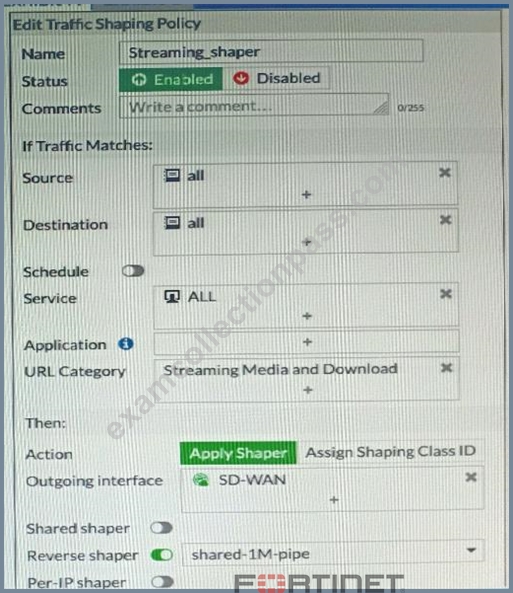
Exhibit B.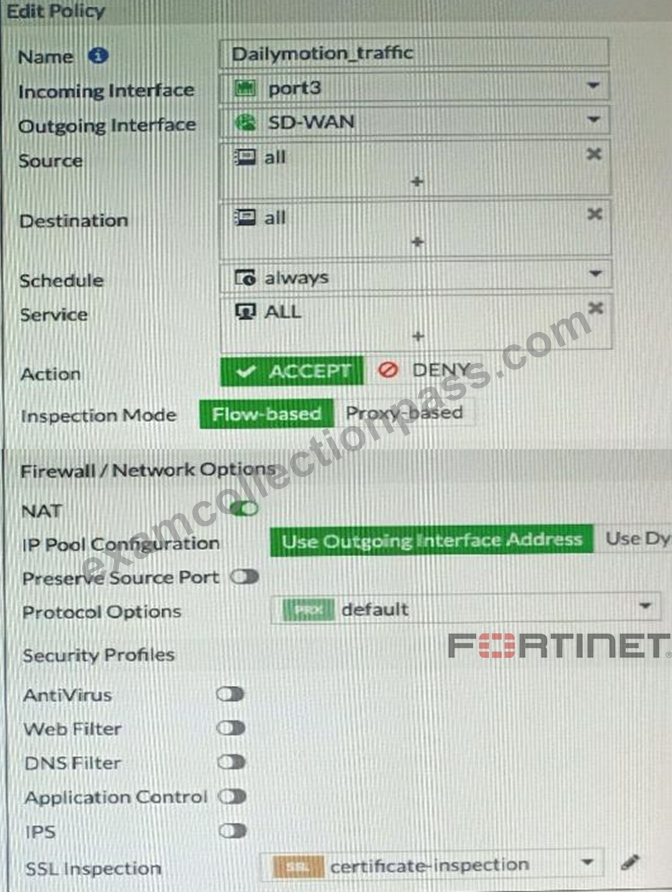
Exhibit A shows the traffic shaping policy and exhibit B show: the firewall policy FortiGate is not performing traffic shaping as expected basi on the policies shown in the exhibits.
To correct this traffic shaping issue on FortiGate, what configuration change must be made on which policy?
- A. The web filter profile must be enabled on the firewall policy
- B. The URL category must be specified on the traffic shaping policy
- C. The application control profile must be enabled on the firewall policy.
- D. The shaper mode must be applied per-IP shaper on the traffic shaping policy
Answer: A
NEW QUESTION 33
Refer to the exhibit.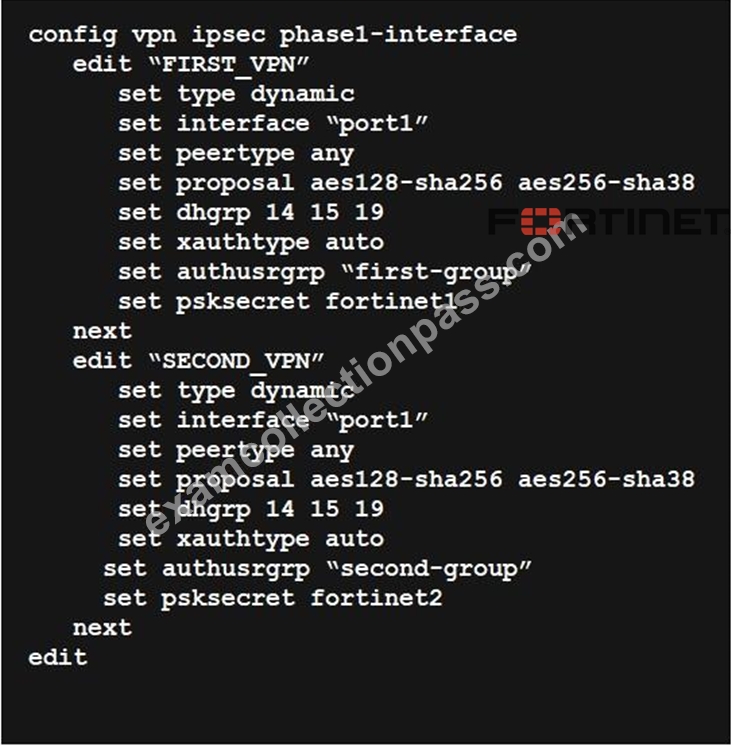
FortiGate has multiple dial-up VPN interfaces incoming on port1 that match only FIRST_VPN.
Which two configuration changes must be made to both IPsec VPN interfaces to allow incoming connections to match all possible IPsec dial-up interfaces? (Choose two.)
- A. Use different proposals are used between the interfaces.
- B. Use unique Diffie Hellman groups on each VPN interface.
- C. Specify a unique peer ID for each dial-up VPN interface.
- D. Configure the IKE mode to be aggressive mode.
Answer: A,B
NEW QUESTION 34
Refer to exhibits.
Exhibit A.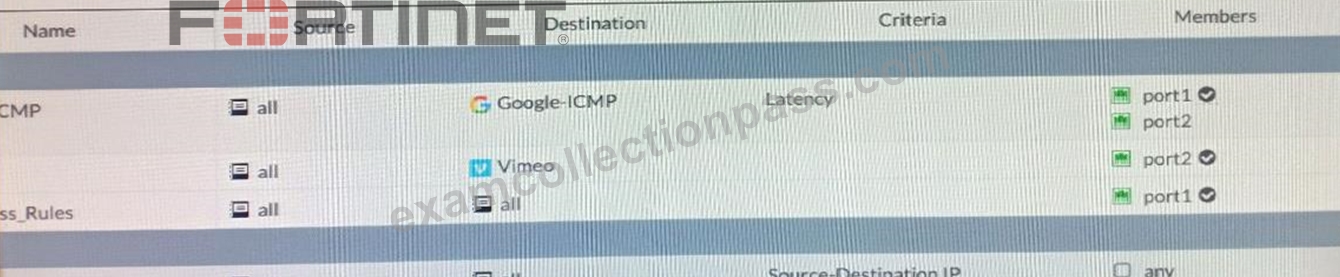
Exhibit B.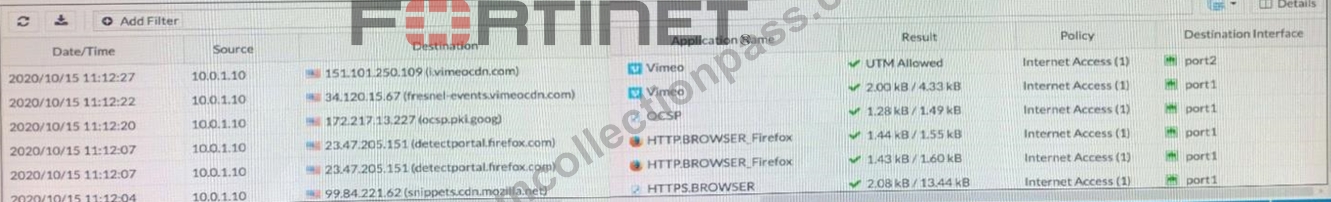
Exhibit A shows the SD-WAN rules and exhibit B shows the traffic logs. The SD-WAN traffic logs reflect how FortiGate processed traffic.
Which two statements about how the configured SD-WAN rules are processing traffic are true? (Choose two.)
- A. SD-WAN rules are evaluated in the same way as firewall policies: from top to bottom
- B. The All_Access_Rules rule load balances Vimeo application traffic among SD-WAN member interfaces
- C. The initial session of an application goes through a learning phase in order to apply the correct rule
- D. The implicit rule overrides all other rules because parameters widely cover sources and destinations.
Answer: C,D
NEW QUESTION 35
Refer to the exhibit.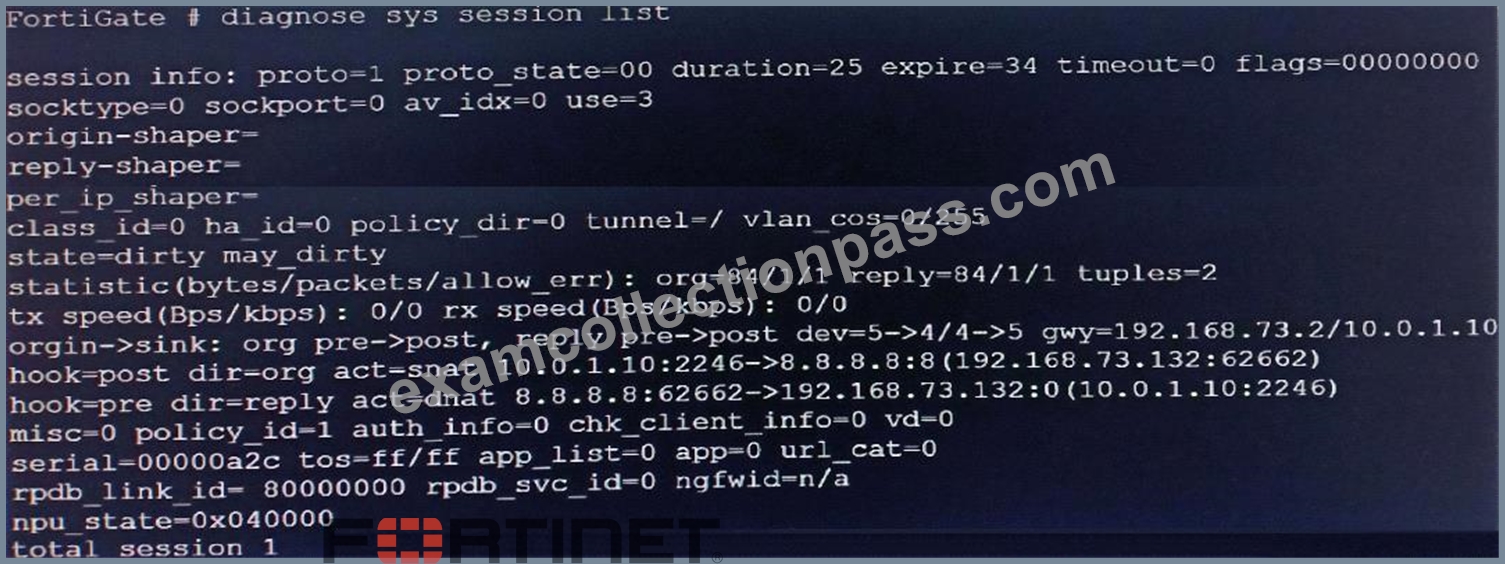
Based on the exhibit, which statement about FortiGate re-evaluating traffic is true?
- A. The type of traffic defined and allowed on firewall policy ID 1 is UDP.
- B. FortiGate has terminated the session after a change on policy ID 1.
- C. Changes have been made on firewall policy ID 1 on FortiGate.
- D. Firewall policy ID 1 has source NAT disabled.
Answer: A
NEW QUESTION 36
Which two reasons make forward error correction (FEC) ideal to enable in a phase one VPN interface? (Choose two )
- A. FEC is useful to increase speed at which traffic is routed through IPsec tunnels.
- B. FEC transmits additional packets as redundant data to the remote device.
- C. FEC improves reliability which overcomes adverse WAN conditions such as noisy links.
- D. FEC transmits the original payload in full to recover the error in transmission.
- E. FEC reduces the stress on the remote device jitter buffer to reconstruct packet loss
Answer: B,C
NEW QUESTION 37
Which three parameters are available to configure SD-WAN rules? (Choose three.)
- A. Application signatures
- B. Type of physical link connection
- C. Source and destination IP address
- D. Internet service database (ISDB) address object
- E. URL categories
Answer: B,C,D
NEW QUESTION 38
Which statement about using BGP routes in SD-WAN is true?
- A. Dynamic routing protocols can be used only with non-encrypted traffic.
- B. VPN topologies must be form using only BGP dynamic routing with SD-WAN.
- C. Learned routes can be used as dynamic destinations in SD-WAN rules.
- D. Adding static routes must be enabled on all ADVPN interfaces.
Answer: C
Explanation:
Explanation/Reference:
https://www.fortinetguru.com/2019/09/using-bgp-tags-with-sd-wan-rules-fortios-6-2/#:~:text=SD%2DWAN%
20rules%20can%20use,to%20the%20customer's%20data%20center.
NEW QUESTION 39
What are two benefits of using FortiManager to organize and manage the network for a group of FortiGate devices? (Choose two )
- A. It improves SD-WAN performance on the managed FortiGate devices.
- B. It simplifies the deployment and administration of SD-WAN on managed FortiGate devices
- C. It sends probe signals as health checks to the beacon servers on behalf of FortiGate
- D. It reduces WAN usage on FortiGate devices by acting as a local FortiGuard server
- E. It acts as a policy compliance entity to review all managed FortiGate devices
Answer: B,D
NEW QUESTION 40
......
Get Top-Rated Fortinet NSE7_SDW-6.4 Exam Dumps Now: https://www.examcollectionpass.com/Fortinet/NSE7_SDW-6.4-practice-exam-dumps.html